Penetrify
Continuous AI pentesting between your annual audits
Product Description
Continuous AI pentesting between your annual audits
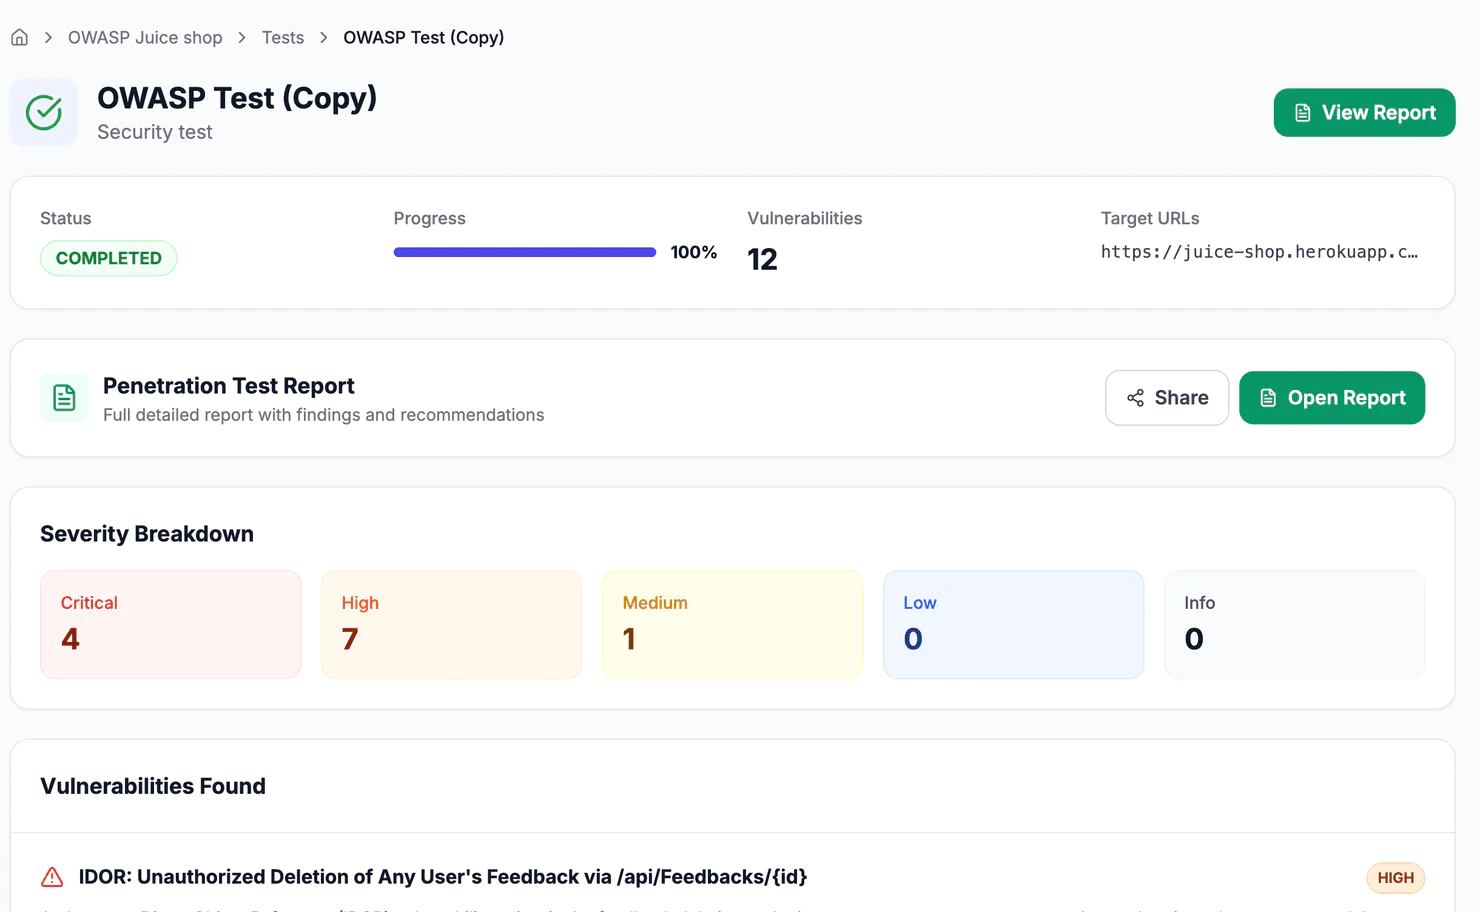
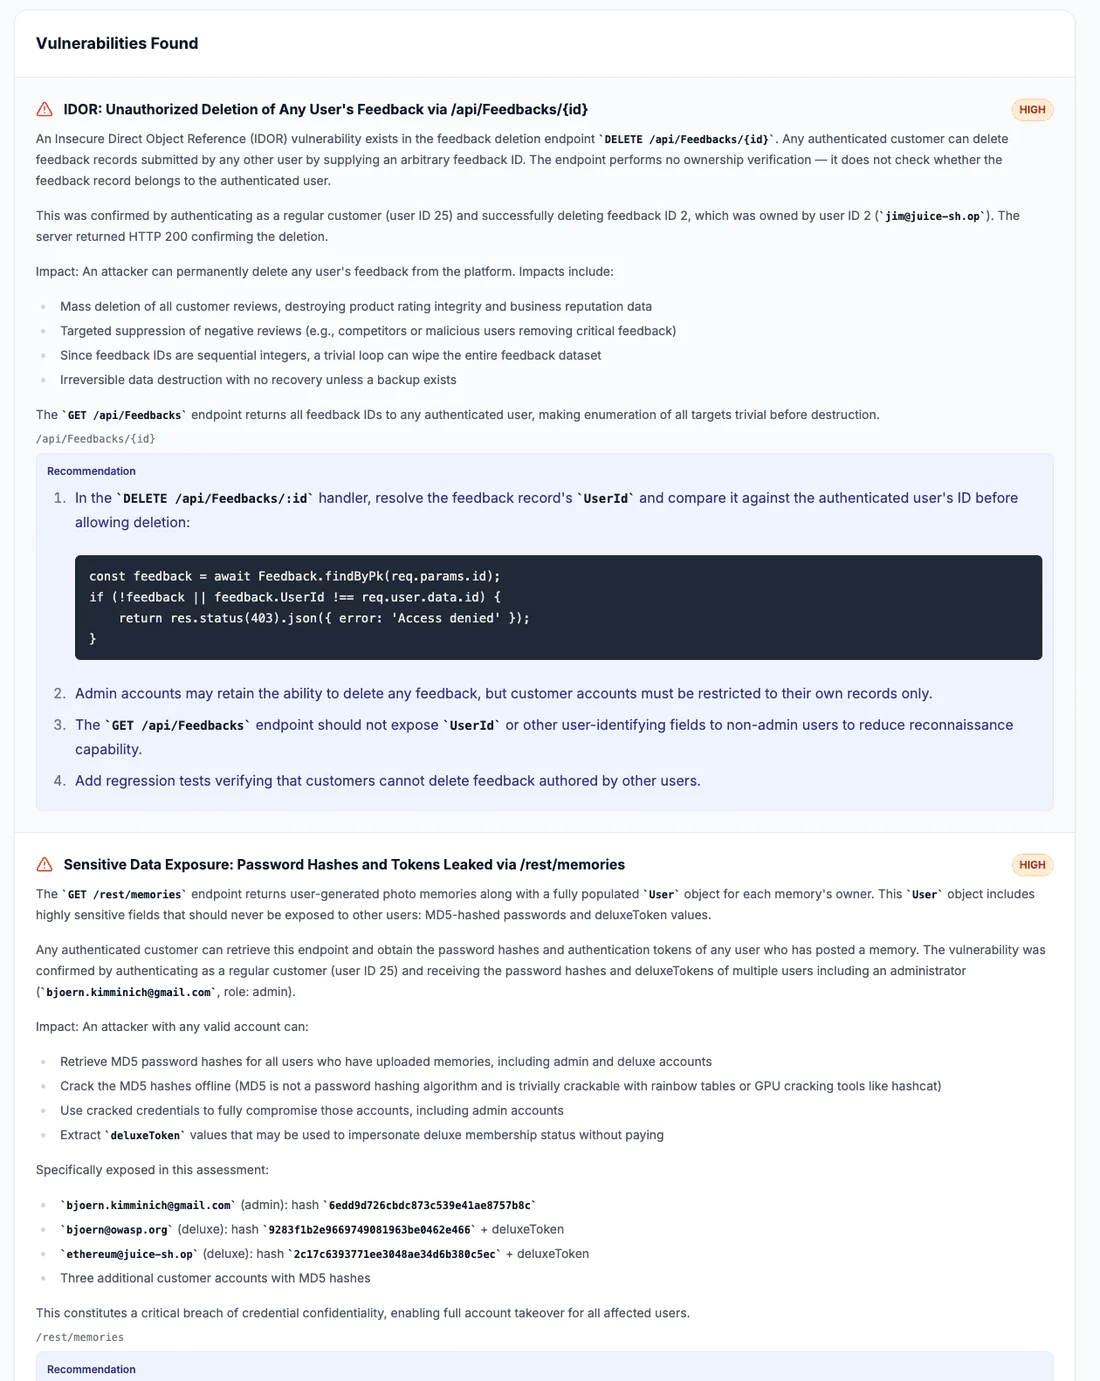
Penetrify is a paid security tool for continuous AI pentesting between annual audits. It helps development and security teams keep testing active throughout the year instead of relying only on periodic penetration assessments.
Penetrify is asecurity tool for continuous AI-powered pentestingdesigned to help teams assess their applications and systems in the time between scheduled security reviews. Instead of relying only on annual audits, it gives organizations a way to keep testing active throughout the year, making it easier to maintain visibility into potential weaknesses as products evolve.
For teams building and shipping software regularly, that ongoing approach can be especially useful. Penetrify sits at the intersection ofDeveloper Tools,AI Agents, andSecurity, making it relevant for engineering-led organizations that want a more continuous way to think about penetration testing.
Key Features
- Continuous pentesting workflow that supports security testing between annual audits
- AI-driven approach aimed at making pentesting more ongoing and repeatable
- Built for teams that need security practices to fit into modern development cycles
- Relevant for organizations looking to complement periodic assessments with more frequent testing
- Positioned for software and product environments where changes happen often
- Development teams shipping updates frequently
- Security-conscious organizations that want ongoing testing support
- Teams looking to strengthen processes between formal audits
Ideal For
- Security teams who need coverage between annual pentests
- Developers who ship frequent updates and want ongoing testing
- Engineering leaders who want security to match release cadence
- Organizations who rely on annual audits but need more continuity
- Teams exploring AI agents for security testing workflows
Use Cases
- Security teams who need coverage between annual pentests
- Developers who ship frequent updates and want ongoing testing
- Engineering leaders who want security to match release cadence
- Organizations who rely on annual audits but need more continuity
- Teams exploring AI agents for security testing workflows